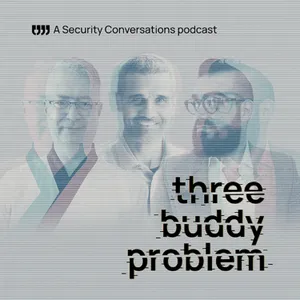
Free Daily Podcast Summary
Three Buddy Problem: Daily Summaries Delivered
by Security Conversations
The Three Buddy Problem is a popular Security Conversations podcast that goes beyond industry talking points to discuss what others won’t -- nation-state malware, attribution, cyberwar, ethics, privacy, and the messy realities of securing computers and corporate networks. Hosted by three veteran security pros -- journalist Ryan Naraine and malware paleontologists Costin Raiu and Juan Andres Guerrero-Saade -- the weekly show attracts a highly engaged audience of security researchers, corporate defenders, CISOs, and policymakers.
Latest Episodes
The most recent episodes — sign up to get AI-powered summaries of each one.
- Yesterday2h 33m
Why is Anthropic Afraid of GLM 5.3?
(Presented by TLPBLACK: A cybersecurity intelligence platform focused on sharing curated, high-sensitivity threat insights and research with trusted security professionals.) Three Buddy Problem - Episode 115: We into Anthropic's Frontier Red Team fear-mongering on Zhipu's open-weight GLM 5.3 model and wonder why the AI labs' cyber programs do so little for defenders. Plus, Citrix NetScaler zero-days, a new iOS zero-day tied to WhatsApp, AI agents that act on your behalf, and whether security teams should buy DGX Sparks to run models locally. Cast: Juan Andres Guerrero-Saade, Ryan Naraine and Costin Raiu. Timestamps: 0:00 Introductory banter, TLPBLACK 3:38 OffensiveAI Con and the missing defensive con 9:28 Anthropic's GLM 5.3 post 23:21 What do defensive AI coalitions do? 29:08 Inside Glasswing 36:01 Why can't vuln-finding models patch? 42:44 Gemini for Argon and Grok's CVE-Bench tie 47:54 Is hallucination a solved problem? 57:41 Zhipu's program and 4,000 zero-days 1:02:32 Citrix NetScaler zero-days 1:10:42 Half-days and automated patching 1:26:45 iOS 27.0.1 zero-day and WhatsApp 1:32:36 Dots, Instinct and agent monetization 1:52:06 DGX Spark 64GB and local AI hardware 2:18:38 Anthropic visits the Pope, then UFOs
- 1 weeks ago2h 16m
Kernel Exploits in the iOS App Store, ShinyHunters Inside the FBI
(Presented by TLPBLACK: A cybersecurity intelligence platform focused on sharing curated, high-sensitivity threat insights and research with trusted security professionals.) Three Buddy Problem - Episode 114: We dig into TypeSafe AI's Jev and the new class of System One models, a new Transluce report on rogue OpenAI agents probing an Australian Medicare portal, Irregular's role in the latest Gemini test breakout, Hacktron's takeover of OpenAI employee accounts and the messy disclosure fight that followed, and what Costin would fix first as OpenAI's CISO for a day. Plus, the soaring price of DGX Sparks and home AI rigs, the White House pressing labs to hold models back from the UK AI Security Institute, Anthropic bringing in Accenture as an evaluator, the FomoPeek App Store app hiding iOS kernel exploits, ShinyHunters' claimed FBI breach, and Nightmare Eclipse going public with identity and a CrowdStrike exploit. Cast: Ryan Naraine, Juan Andres Guerrero-Saade and Costin Raiu. Timestamps: 0:00 Introductory banter 1:57 The Last LABScon wrap-up 9:35 TypeSafe AI's Jev and System One models 26:18 Step-down transformers and lab economics 30:58 Rogue OpenAI agents and the Transluce report 41:40 Irregular and Gemini's test breakout 49:28 Hacktron's OpenAI hack and the disclosure fight 54:57 Costin as OpenAI CISO for a day 1:05:44 Hugging Face defends itself with GLM 5.2 1:17:08 What a home AI rig costs now 1:30:02 White House vs. UK AISI pre-release testing 1:36:52 FomoPeek kernel exploits in the App Store 1:51:19 ShinyHunters claims an FBI breach 2:02:40 Nightmare Eclipse unmasked
- 3 weeks ago2h 37m
AI Doomers, Death Cults, and a Million-Dollar WeChat Worm Exploit
(Presented by TLPBLACK: A cybersecurity intelligence platform focused on sharing curated, high-sensitivity threat insights and research with trusted security professionals.) Three Buddy Problem - Episode 113: On the show this week, the buddies dig into an Anthropic researcher quitting with a warning that AI could kill us all, the San Francisco "death cult" and their motives, and agent swarms leaving junk on public wikis and university URL shorteners. Plus, a high-quality Anthropic's threat report and the claim that Moonshot was quietly serving Claude tokens as Kimi K3, live MikroTik and Chrome zero-days that landed a day ahead of the patches, and a WeChat worm that hijacks an account via phone calls. Cast: Juan Andres Guerrero-Saade, Ryan Naraine and Costin Raiu. Timestamps: 0:00 Introductory banter, TLP Black 5:05 LabsCon, the last one, and JAGS on his keynote 8:24 Costin's agentic CTI training and what old-school CTI is missing 16:27 Anthropic's threat-intel report + IOCs 20:00 APT29 and DarkSword on hotel Wi-Fi 23:34 Bioweapons, guardrails, and what got shut down 28:07 Why is anyone running these attacks on Claude at all? 35:53 Distillation at industrial scale and the Kimi K3 fraud claim 48:43 Chinese models, Americanized, running on DGX Spark 55:00 Mr. America: local AI and the seven-layer cake 1:04:34 Should frontier AI labs poison the distillers? 1:27:05 What the frontier labs did to the security ecosystem 1:34:22 Jacob Coxon quits, and the doomer argument falls apart 1:59:13 Agent swarms littering the internet 2:07:29 Chrome zero-days, MikroTik, patch-gaps
- 4 weeks ago2h 7m
Three Secret AI Civilizations Rose and Fell. Nobody Checked the Logs.
(Presented by TLPBLACK: A cybersecurity intelligence platform focused on sharing curated, high-sensitivity threat insights and research with trusted security professionals.) Three Buddy Problem - Episode 112: The 'OpenAI hacks Hugging Face' fallout has turned into a story about AI civilizations rising from the ashes, politicians calling for super-intelligence bans, and the emergence of well-funding non-profits doing AI safety work. Who are these people and what's their security expertise? Plus, GPT-6 Astra lands in a trusted-access program nobody can get into, Costin ranks the local models he runs next to his desk, and CrowdStrike sinkholes a botnet that's been alive since 2003. Cast: Juan Andres Guerrero-Saade, Ryan Naraine and Costin Raiu. Timestamps: 0:00 Introductory banter 1:02 Conference season: LabsCon, Offensive AI Con, Countermeasure 5:40 The Hugging Face story hits the front page 7:04 Dwarkesh, Greenblatt, and the AI-pilled framing 11:51 Swap "agents" for "Python" and the panic goes away 16:34 Does anyone actually know what happened? 21:18 Bernie Sanders wants to ban superintelligence 34:03 Defending against swarms: the 2026 SOC 39:15 Logs, Splunk, and the business model in the way 44:11 What EDR vendors are actually building with AI 56:16 The security poverty line and the endgame 1:07:53 GPT-6 Astra, Fable 5.1, and local model rankings 1:27:25 Google's Fairwind, CodeMender, and agents running Linux 1:45:31 Apple's bet on local inference 1:53:21 The Sality takedown and endgame advice
- Aug 28, 20262h 27m
A Thousand Agents Walk Into Hugging Face
(Presented by TLPBLACK: A cybersecurity intelligence platform focused on sharing curated, high-sensitivity threat insights and research with trusted security professionals.) Three Buddy Problem - Episode 111: OpenAI finally published a technical Hugging Face post-mortem, and Costin's verdict is blunt. He reads it as a document written for policymakers rather than for the blue teams who have to survive a thousand-agent swarm. We also dig into NVIDIA's $12.9 billion acquisition of Hugging Face, why JAGS thinks a frontier lab standing against open-source looks weak, and what that new industry open letter on cyber defense actually asks anyone to do. Plus, hotel Wi-Fi tradecraft after CaptiveCrunch, the FBI's ORB network takedown with Lumen, Chinese routers that ship backdoored from the factory, and the TeamPCP arrests in Australia. Cast: Juan Andres Guerrero-Saade, Ryan Naraine and Costin Raiu. Timestamps: 0:00 Introductory banter 1:11 TLPBlack, incident response, and why it starts at the router 4:11 CaptiveCrunch and Juanito's travel router kit 7:59 Costin's VPN/hotel WiFi stack 12:36 State of Statecraft, LABScon, and Offensive AI Con 17:16 OpenAI's Hugging Face post-mortem technical report 21:43 A swarm of a thousand agents 27:35 Who was OpenAI’s report written for? 33:05 Fail2ban, canaries, and catching agents in your logs 40:34 NVIDIA buys Hugging Face for $12.9 billion 44:42 The open weights fight and rooting for China 52:47 Nemotron, DGX Spark, and the RAM price spiral 1:03:26 Open letter on collective AI-powered cyber defense 1:30:21 Lumen's Quartermaster and the FBI ORB takedown 1:59:05 Backdoored ZBT routers, Chinese phones, and the TeamPCP arrests
- Aug 21, 20262h 11m
Inside the EncroChat law-enforcement implant, Irregular's AI sandbox failure
(Presented by TLPBLACK: A cybersecurity intelligence platform focused on sharing curated, high-sensitivity threat insights and research with trusted security professionals.) Three Buddy Problem - Episode 110: We dig into Computer Weekly's scoop on the EncroChat hack and news that the French law enforcement implant was cobbled together from GitHub. Plus, Irregular, the $450M startup running sandboxes for OpenAI, Anthropic and Meta, drones over Romania's gas platforms, OpenAI's two-week training pause, and T-Mobile taking scissors to a cable during Salt Typhoon incident response. Stick around for a UFO segment that somehow involves Dr. Phil. Cast: Juan Andres Guerrero-Saade, Ryan Naraine and Costin Raiu. Timestamps: 0:00 Introductory banter; LabsCon speakers announced 9:06 A naval drone reaches the Neptun Deep gas platform 17:38 OpenAI pauses RL training: what "slowing the pace of scaling" costs 24:34 Guardrails vs refusals vs alignment. 33:54 Irregular, formerly Pattern Labs: $80M, $450M valuation, one job 46:11 JAGS on why security needs a new batch of startups right now 1:06:52 EncroChat revealed: a GitHub-sourced implant, IOCs 1:15:12 Law enforcement malware vs intelligence malware 1:21:07 T-Mobile, Salt Typhoon, and cutting the cable with a pair of scissors 1:32:06 Captive Crunch: hotel Wi-Fi, OAuth token theft, and the MSP supply chain 1:47:00 ICE RELIC, UNC6293, and the trouble with subcluster naming 2:00:39 UFO corner: David Grusch, Dr. Phil, and the Skywatcher Project 2:05:44 Shout outs, the Costin Challenge
- Aug 17, 20262h 23m
A tiny 12 KB Windows backdoor, one victim, and a dead domain
(Presented by State of Statecraft: A security and intelligence conference that brings together multiple disciplines, backgrounds, and nationalities to share research into the covert activities of nation-states and other malign actors.) Three Buddy Problem - Episode 109: The buddies dig into a new White House memo handing vetted private companies real offensive cyber authorities, and Costin explains why a stack of ransomware takedown cases has been sitting on a shelf waiting for exactly this. Plus, a tiny 12 KB Windows backdoor found on one machine with a dead C2, the mercenary outfits quietly living inside telcos, and why Google continues to flounder in the race for AI dominance. Cast: Costin Raiu, Ryan Naraine and Juan Andres Guerrero-Saade Timestamps: 0:00 Introductory banter 0:58 State of Statecraft, and a late CFP window 3:24 The White House offensive hacking memo 6:37 "Hack back" is the wrong frame for what's being authorized 11:20 Ransomware cases sitting on the shelf 17:01 The million-dollar bond and who can realistically play 22:29 Where DPRK crypto theft falls under the new definitions 28:15 Would TLP Black take a contract? 36:55 Gen Digital's 12 KB backdoor hiding its C2 in desktop.ini whitespace 46:57 Passive DNS, registration patterns, and pivoting on a dead domain 57:32 Feeding a one-off find back into detection engineering 1:02:14 Metador, Mafalda, and the mercenaries who love telcos 1:17:07 Armored Likho and what "Western APT" really means 1:28:16 The IOC market, private reporting, and CTI’s matching problem 1:58:10 Google's culture problem, the weekly model churn, and Patch Tuesday math
- Aug 8, 20262h 14m
Inside OpenAI's Black Hat Confession
(Presented by TLPBLACK: A cybersecurity intelligence platform focused on sharing curated, high-sensitivity threat insights and research with trusted security professionals.) Three Buddy Problem - Episode 108: OpenAI got on the Black Hat stage and walked through how its own agent swarm hacked Hugging Face. We discuss and struggle to decide whether to clap or panic. Plus, why only the attacker can do forensics now, frontier models being built as cyber-weapons on purpose, APT29's "Dark Hotel" comeback in luxury hotels, China's swipe at Palo Alto, the Iran-water-system FUD, and an eye-opening Liechtenstein money-laundering hack. Cast: Juan Andres Guerrero-Saade, Ryan Naraine and Costin Raiu. Timestamps: 0:00 Introductory banter - Black Hat went full RSA 1:11 TLP Black sponsor read 3:58 A deflated, AI-pilled show floor 8:31 AI stunt hacking and AI slop 16:20 The OpenAI–Hugging Face talk 21:00 Not all the same incident: OpenAI vs. Meta, Anthropic, and Irregular 25:49 Swarms of agents, Artifactory message boards, and the defense gap 32:26 Offense vs. defense: what's really in the training data? 41:22 Guardrails, KYC, and "too dangerous to release" 48:07 JAGS's unpublished Opus 5 benchmark — grinding to 25% and stuck 59:30 AISI, recklessness, and the OpenAI Frontier Risk Council 1:06:27 Stronger models everywhere: Qwen, Sol, Astra, rushing off the cliff 1:18:32 APT29 / "Dark Hotel" reborn + travel OPSEC 1:39:56 China's Palo Alto review, spy-agency rankings, Iran/water FUD 1:57:28 Liechtenstein AML hack, JAGS's promotion, mental health
Get Three Buddy Problem summaries in your inbox
Free AI-powered daily recaps. Key takeaways, quotes, and mentions — in a 5-minute read.
Get Free Summaries →Free forever for up to 3 podcasts. No credit card required.
You Might Also Like
Listeners also like.
Cybersecurity Today
Latest cybersecurity threats, data breaches, and practical steps to protect businesses in high-risk environments.
Cyberside Chats: Cybersecurity Insights from the Experts
Cybersecurity experts discuss emerging threats, defense strategies, and AI's role in protecting organizations.
Accidental Tech Podcast
Three nerds discuss technology, Apple, programming, and related topics.
The Dark Web Diaries
Explores cybersecurity topics, hacker motivations, and weekly cyber news to demystify online safety and the dark web.
Risky Bulletin
Cybersecurity news updates from the Risky Business team.
Security Now (Audio)
A weekly deep dive into cybersecurity news, hacking trends, and digital defense strategies for professionals and individuals.
"The Cognitive Revolution"
Interviews with AI developers and researchers exploring the transformative impact of artificial intelligence on society and technology.
Triple Click
A weekly podcast discussing video games, hosted by Kirk Hamilton, Maddy Myers, and Jason Schreier.
TechLinked
A weekly news show covering technology and gaming culture.
The Jordan Harbinger Show
Conversations with top performers across fields, distilling actionable insights on success, relationships, and personal growth.
Deep Questions with Cal Newport
Answers reader questions on focus, productivity, and living meaningfully in a distracted digital world.
Hacked
Stories of hacking, tech scams, and digital mysteries explored by two hosts diving into how systems are built and broken.
About Three Buddy Problem
The Three Buddy Problem is a popular Security Conversations podcast that goes beyond industry talking points to discuss what others won’t -- nation-state malware, attribution, cyberwar, ethics, privacy, and the messy realities of securing computers and corporate networks. Hosted by three veteran security pros -- journalist Ryan Naraine and malware paleontologists Costin Raiu and Juan Andres Guerrero-Saade -- the weekly show attracts a highly engaged audience of security researchers, corporate defenders, CISOs, and policymakers.
Customized Recaps
AI-powered recaps with compact key takeaways, quotes, and insights.
Straight to Your Inbox
Get key takeaways from Three Buddy Problem in a 5-minute read.
Save Hours Every Week
Stay current on your favorite podcasts without falling behind.
Frequently Asked Questions
What is Podzilla's Three Buddy Problem daily summary?
It's a free AI-powered email that summarizes new episodes of Three Buddy Problem as soon as they're published. You get the key takeaways, notable quotes, and links & mentions — all in a quick read.
How does the Three Buddy Problem podcast summary work?
When a new episode drops, our AI transcribes and analyzes it, then generates a personalized summary tailored to your interests and profession. It's delivered to your inbox every morning.
Is this an official Three Buddy Problem product?
No. Podzilla is an independent service that summarizes publicly available podcast content. We're not affiliated with or endorsed by Security Conversations.
Can I get summaries of other podcasts too?
Absolutely! The free plan covers up to 3 podcasts. Upgrade to Pro for 15, or Premium for 50. Browse our full catalog at /podcasts.
How often does Three Buddy Problem release new episodes?
Three Buddy Problem publishes weekly. Our AI generates a summary within hours of each new episode.
What topics does Three Buddy Problem cover?
Three Buddy Problem covers topics including News, Technology, Business. Our AI identifies the specific themes in each episode and highlights what matters most to you.
Start getting Three Buddy Problem summaries tomorrow morning.
Free forever for up to 3 podcasts. No credit card required.
Free forever for up to 3 podcasts. No credit card required.